
MATH 261 Final, Fall 2005
American University of Beirut · Number Theory · 1 page
Stuck on a question? A tutor can walk you through it.
More MATH 261 files
Show the text of this final exam
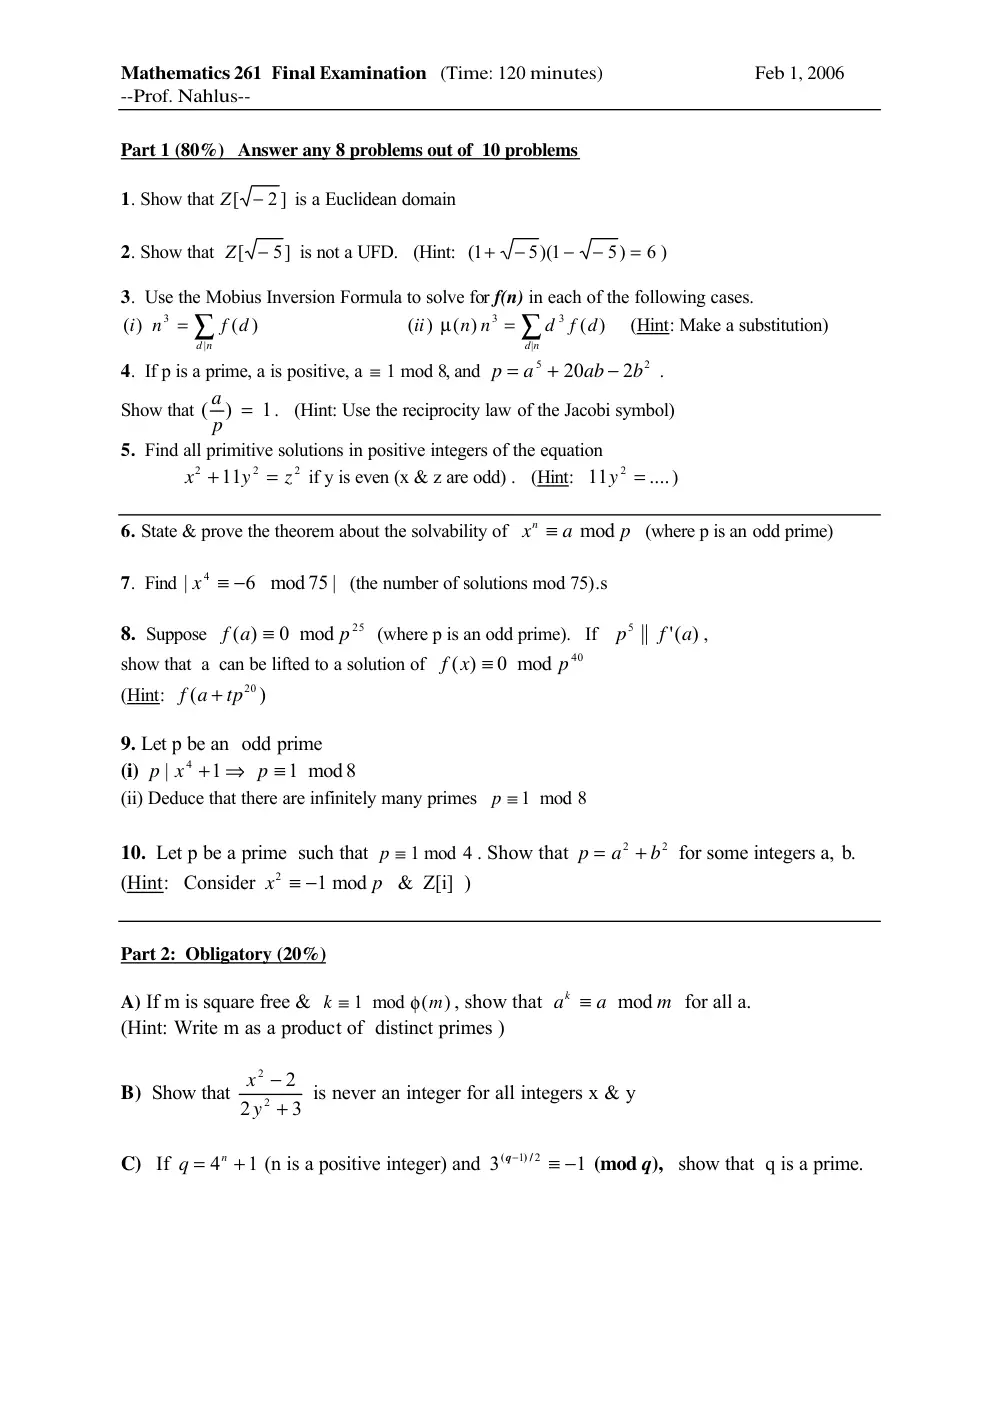
Mathematics 261 Final Examination (Time: 120 minutes)
Feb 1, 2006
--Prof. Nahlus--
Part 1 (80%) Answer any 8 problems out of 10 problems
1. Show that
Z[ − 2 ]
is a Euclidean domain
2. Show that
Z[ − 5]
is not a UFD. (Hint:
6
5)
5)(1
1(
=
−
−
−
+
)
3. Use the Mobius Inversion Formula to solve for f(n) in each of the following cases.
∑
∑
=
=
d n
d n
f d
d
n n
ii
f d
n
i
|
3
3
|
3
( )
( )
( )
( )
( )
µ
(Hint: Make a substitution)
4. If p is a prime, a is positive, a ≡ 1 mod 8, and
2
5
2
20
b
ab
a
p
−
+
=
.
Show that (
a )
p
= 1. (Hint: Use the reciprocity law of the Jacobi symbol)
5. Find all primitive solutions in positive integers of the equation
2
2
2
11
z
y
x
=
+
if y is even (x & z are odd) . (Hint:
....
11
y2 =
)
6. State & prove the theorem about the solvability of
p
a
xn
mod
≡
(where p is an odd prime)
7. Find
6 mod 75 |
|
4
≡ −
x
(the number of solutions mod 75).s
8. Suppose
25
0 mod
( )
p
f a
≡
(where p is an odd prime). If
)
('
5 ||
a
f
p
,
show that a can be lifted to a solution of
40
0 mod
( )
p
f x
≡
(Hint:
)
(
tp20
f a
+
9. Let p be an odd prime
(i)
1 mod 8
1
|
4
≡
+ ⇒
p
x
p
(ii) Deduce that there are infinitely many primes
p ≡ 1 mod 8
10. Let p be a prime such that
p ≡ 1 mod 4
. Show that
2
2
b
a
p
+
=
for some integers a, b.
(Hint: Consider
p
x
1 mod
2
≡ −
& Z[i] )
Part 2: Obligatory (20%)
A) If m is square free &
)
(
1 mod
m
k
φ
≡
, show that
m
a
ak
mod
≡
for all a.
(Hint: Write m as a product of distinct primes )
B) Show that
3
2
2
2
2
+
−
y
x
is never an integer for all integers x & y
C) If
= 4 +1
n
q
(n is a positive integer) and
),
(mod
) /
(
q
q
1
3
1 2
≡ −
−
show that q is a prime.