
CSC 316 Chapter, Spring 2004
Notre Dame University–Louaize · Computers Security and Their Data · 25 pages · Dr. Victor Sawma

Showing the first 10 of 25 pages. Download the PDF to see all of it.
More CSC 316 files
Show the text of this chapter
1
Intrusion Detection Systems
An Overview
2
Agenda
Background and Necessity
Firewalls
Intrusion Detection Systems (IDS)
Introduction and Benefits
Difference between Firewall and IDS
Types of IDS
Intrusion Detection Techniques
Unrealistic Expectations
3
Historical Facts
May 1996, 10 major agencies, comprising 98% of
Federal Budget were attacked with 64%
64% of attack
success rate
Feb 2000, DOS
DOS attacks against world’s largest
commercial web sites including yahoo.com and
amazon.com.
July 2001, Code Red
Code Red virus sweeps across the whole
world infecting 150,000
150,000 computers in just 14
14
hours.
Sept
2001,
NIMDA
NIMDA
virus
expands
itself
to
computers all across US, lasts for days and attacks
over 80,000
80,000 computers
4
Points to Ponder
Typical businesses spend only about 0.15% of
annual sales on the security needs of their
corporate network [1]
This amount is even less than most of these companies
This amount is even less than most of these companies
spend on coffee for the staff
spend on coffee for the staff
60% of firms do not have a clue about how much
these security breaches are costing them [2]
Approximately 70 percent of all cyber attacks on
Approximately 70 percent of all cyber attacks on
enterprise systems are believed to be
enterprise systems are believed to be
perpetrated by trusted insiders
perpetrated by trusted insiders
5
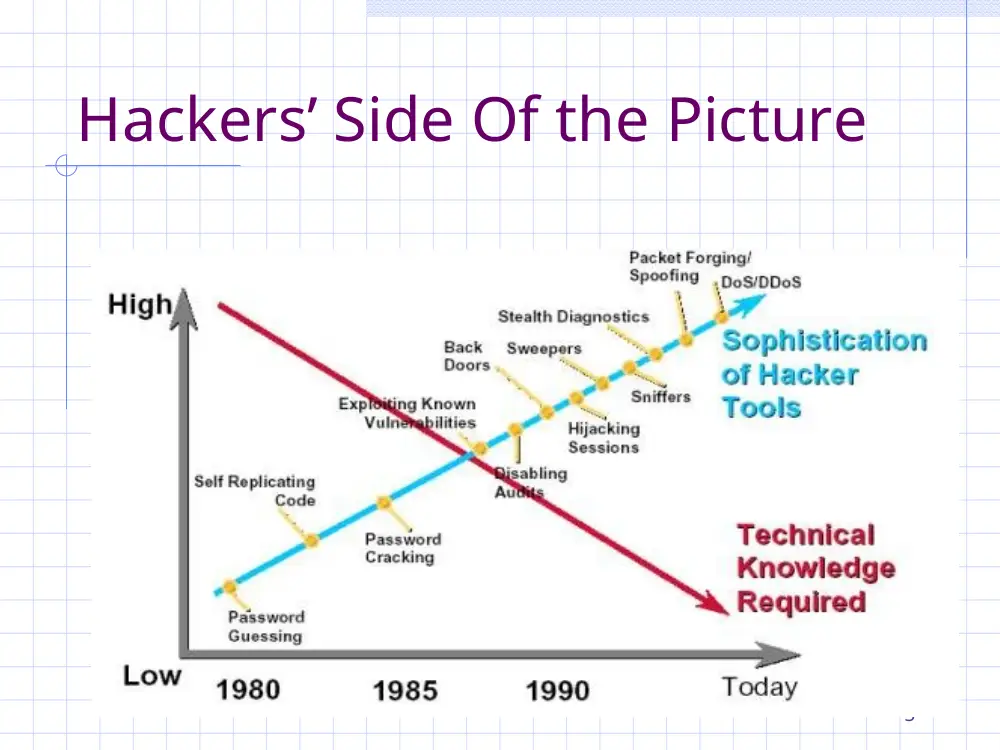
Hackers’ Side Of the Picture
6
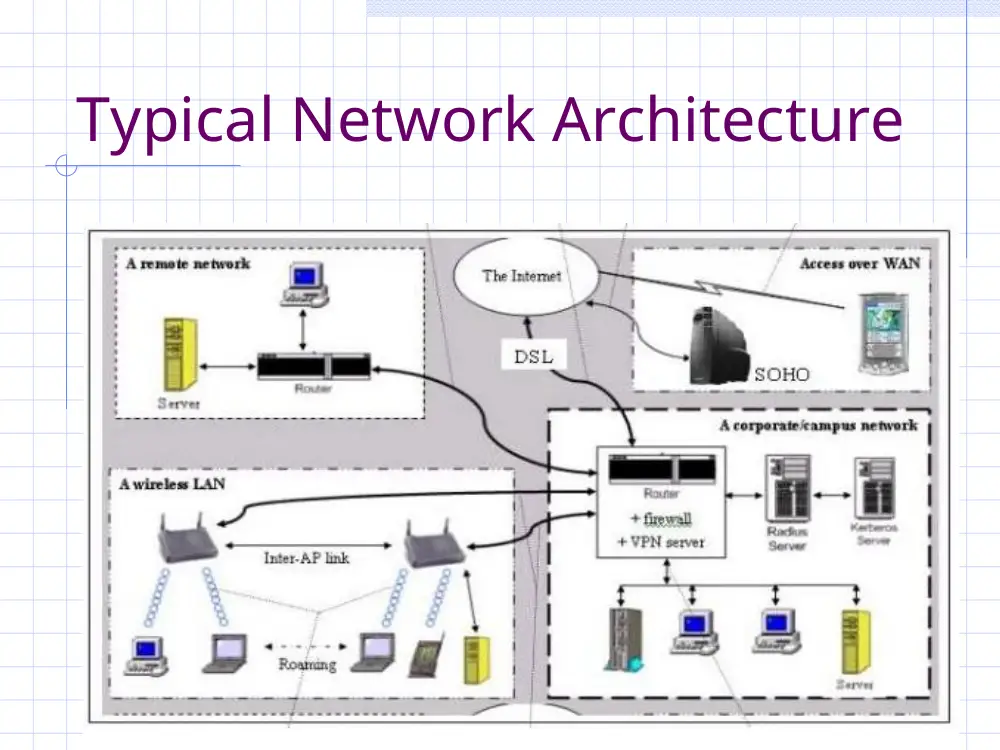
Typical Network Architecture
7
First Line of Defense:
The Firewall
Primary means of securing a private network
against penetration from a public network
An access control device, performing perimeter
security by deciding which packets are allowed or
denied, and which must be modified before passing
Core of enterprise’s comprehensive security policy
Can monitor all traffic entering and leaving the
private network, and alert the IT staff to any
attempts to circumvent security or patterns of
inappropriate use
8
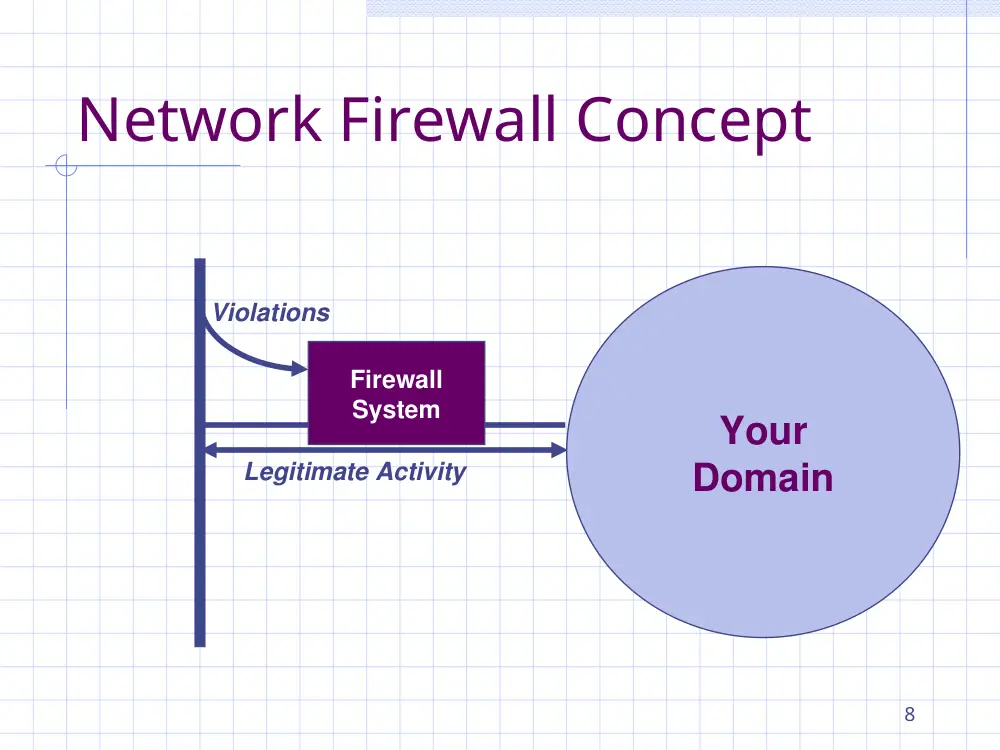
Network Firewall Concept
Firewall
System
Your
Domain
Legitimate Activity
Violations
9
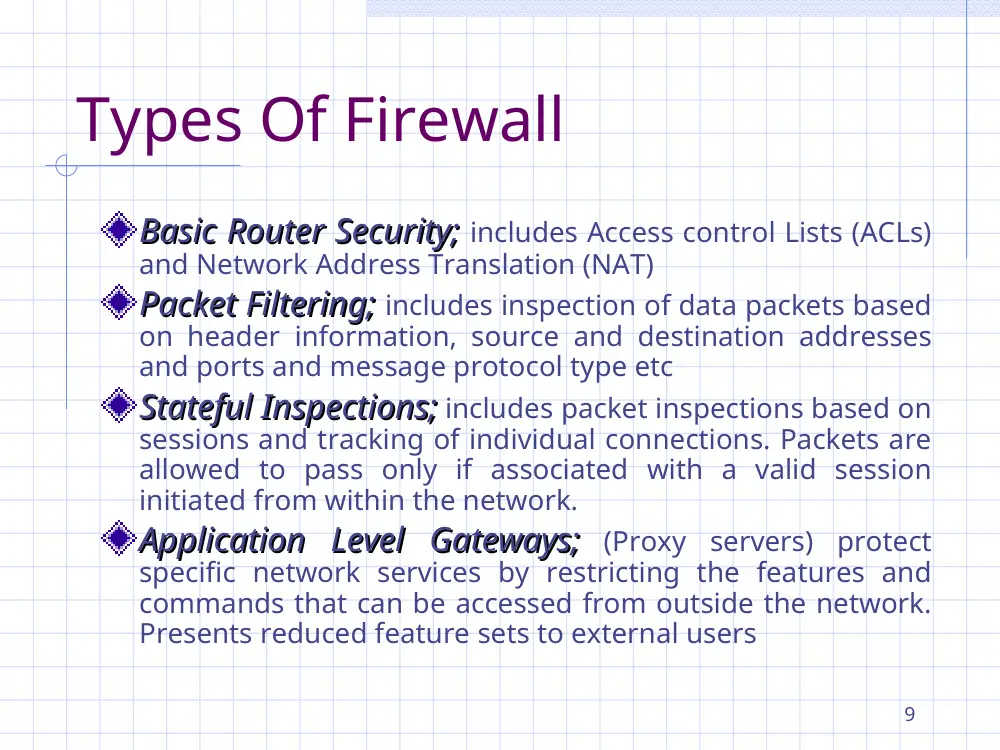
Types Of Firewall
Basic Router Security;
Basic Router Security; includes Access control Lists (ACLs)
and Network Address Translation (NAT)
Packet Filtering;
Packet Filtering; includes inspection of data packets based
on header information, source and destination addresses
and ports and message protocol type etc
Stateful Inspections;
Stateful Inspections; includes packet inspections based on
sessions and tracking of individual connections. Packets are
allowed to pass only if associated with a valid session
initiated from within the network.
Application Level Gateways;
Application Level Gateways; (Proxy servers) protect
specific network services by restricting the features and
commands that can be accessed from outside the network.
Presents reduced feature sets to external users
10
Introduction to IDS
IDSs prepare for and deal with attacks by collecting
information from a variety of system and network
sources, then analyzing the symptoms of security
problems
IDSs serve three essential security functions;
monitor
monitor, detect
detect and respond
respond to unauthorized activity
IDS can also respond automatically (in real-time) to a
security breach event such as logging off a user,
disabling a user account and launching some scripts
11
Some of the benefits of IDS
monitors the operation of firewalls, routers, key
management servers and files critical to other security
mechanisms
allows administrator to tune, organize and comprehend
often incomprehensible operating system audit trails and
other logs
can make the security management of systems by non-
expert staff possible by providing nice user friendly interface
comes with extensive attack signature database against
which information from the customers system can be
matched
can recognize and report alterations to data files
12
FIREWALLS VS IDSs
13
FIREWALL VS IDS (cont)
Firewall cannot detect security breaches associated
with traffic that does not pass through it. Only IDS is
aware of traffic in the internal network
Not all access to the Internet occurs through the
firewall.
Firewall does not inspect the content of the permitted
traffic
Firewall is more likely to be attacked more often than
IDS
Firewall is usually helpless against tunneling attacks
IDS is capable of monitoring messages from other
pieces of security infrastructure
14
TYPES OF IDS
1. HOST – BASED (HIDS)
2. NETWORK – BASED (NIDS)
3. HYBRID
15
HIDS
works in switched network environments
operates in encrypted environments
detects and collects the most relevant
information
in
the
quickest
possible
manner
tracks behavior changes associated with
misuse.
requires the use of the resources of a host
server – disk space, RAM and CPU time
Does not protect entire infrastructure
16
NIDS
PASSIVE Interface to Network Traffic
17
NIDS (cont)
Sensor Placement
18
NIDS (cont)
Advantages
NIDS uses a passive interface to capture network
packets for analyzing.
NIDS sensors placed around the globe can be
configured to report back to a central site, enabling a
small team of security experts to support a large
enterprise.
NIDS systems scale well for network protection
because the number of actual workstations, servers, or
user systems on the network is not critical – the
amount of traffic is what matters
Most network-based IDSs are OS-Independent
Provide better security against DOS attacks
19
NIDS (cont)
Disadvantages
Cannot scan protocols or content if network traffic
is encrypted
Intrusion detection becomes more difficult on
modern switched networks
Current network-based monitoring approaches
cannot efficiently handle high-speed networks
Most of Network-based systems are based on
predefined attack signatures--signatures that will
always be a step behind the latest underground
exploits
20
HYBRID
Although the two types of Intrusion Detection
Systems differ significantly from each other, but
they also complement each other.
Such a system can target activity at any or all
levels
It is easier to see patterns of attacks over time and
across the network space
No proven industry standards with regards to
interoperability of intrusion detection components
Hybrid systems are difficult to manage and deploy
21
INTRUSION DETECTION
TECHNIQUES
MISUSE DETECTION (SIGNATURE
MISUSE DETECTION (SIGNATURE
ANALYSIS)
ANALYSIS)
1.
PATTERN MATCHING
2.
STATEFUL PATTERN MATCHING
3.
PROTOCOL DECODE BASED ANALYSIS
4.
HEURISTIC BASED ANALYSIS
TARGET MONITORING
TARGET MONITORING
22
INTRUSION DETECTION
TECHNIQUES (cont)
ANOMALY DETECTION
ANOMALY DETECTION
1. STATISTICAL APPROACH
2. PREDICTIVE PATTERN GENERATION
3. NEURAL NETWORKS
STEALTH PROBES
STEALTH PROBES
23
IDS is not a SILVER BULLET
SILVER BULLET
cannot conduct investigations of attacks
without human intervention
cannot
intuit
the
contents
of
your
organizational security policy
cannot
compensate
for
weaknesses
in
network protocols
cannot compensate for weak identification
and authentication mechanisms
capable of monitoring network traffic but to a
certain extent of traffic level
24
References
[1] “Inoculating The Network”
By Mathias Thurman
EBSCO HOST Research Databases
[2] National Strategy To Secure Cyberspace
Draft September 2002
www.securecyberspace.gov
[3] An Introduction to Intrusion Detection / Assessment
By Rebecca Bace
http://www.icsalabs.com
[4] White paper on “The Science Of Intrusion Detection System
– Attack Identification”
http://www.cisco.com
25
References (cont)
[5] “An Introduction To Intrusion Detection Systems”
By Paul Innella and Oba McMillan, Tetrad Digital Integrity, LLC
http://www.securityfocusonline.com/
[6] “Intrusion Detection and Prevention Product Update”
By Joel McFarland
Speaker Presentations at http://www.cisco.com
[7] “An Introduction to Intrusion Detection”
By Aurobindo Sundaram
http://www.acm.org
[8] White paper on “Internet Security for Small Businesses”
http://www.cisco.com
[9] Presentation on Firewalls by Tom Longstaff
Cert Coordination Center - Carnegie Mellon University
http://www.andrew.cmu.edu/course/95-750/yihudoc/Lecture6.ppt